Passive fire protection · penetration seals

From the customer's enquiry to the owner's handover, every step checked against the tested configuration.

Gennemført 2.0 formalises the fire adviser's work. Enquiries are pre-checked against 678 tested rows from two ETAs while the customer types. Deviations go through a case workflow with precedents, four-eyes review and a hash-chained audit trail. Issued assessments, quotes, site records and handover packages can all be verified, file by file.

IFC4ETA-21/0110 + ETA-20/1322BCF 2.1MCPMIT
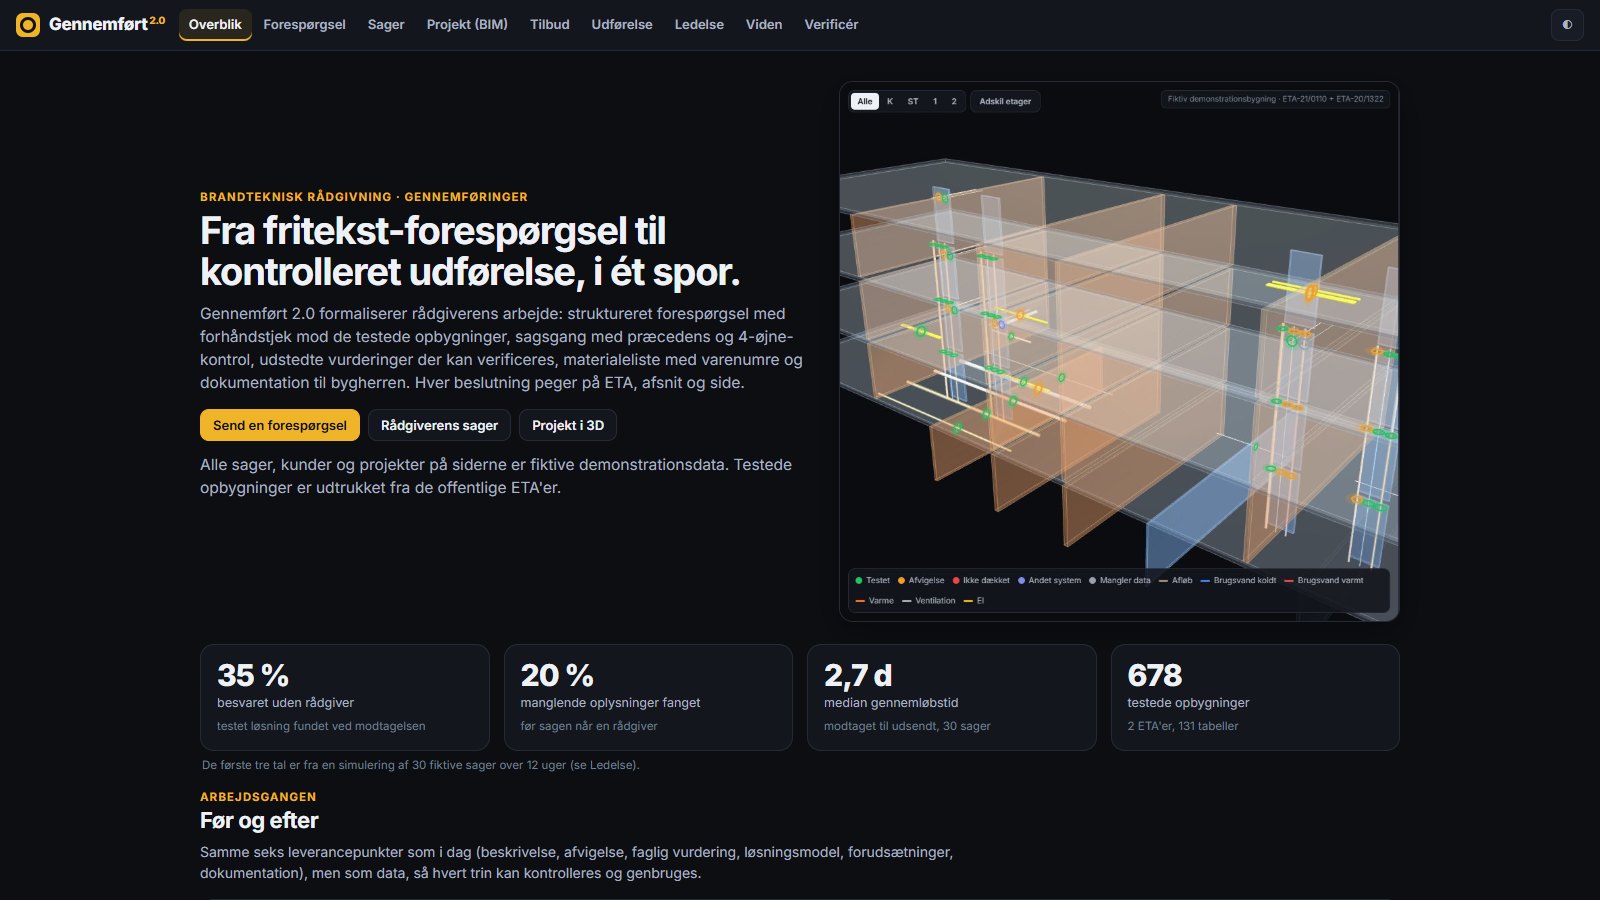
Live 3D register · fictitious demo building
0tested ETA rows, page and row cited
0answer key, hand-derived from the ETA pages
0browser = server, every check's text
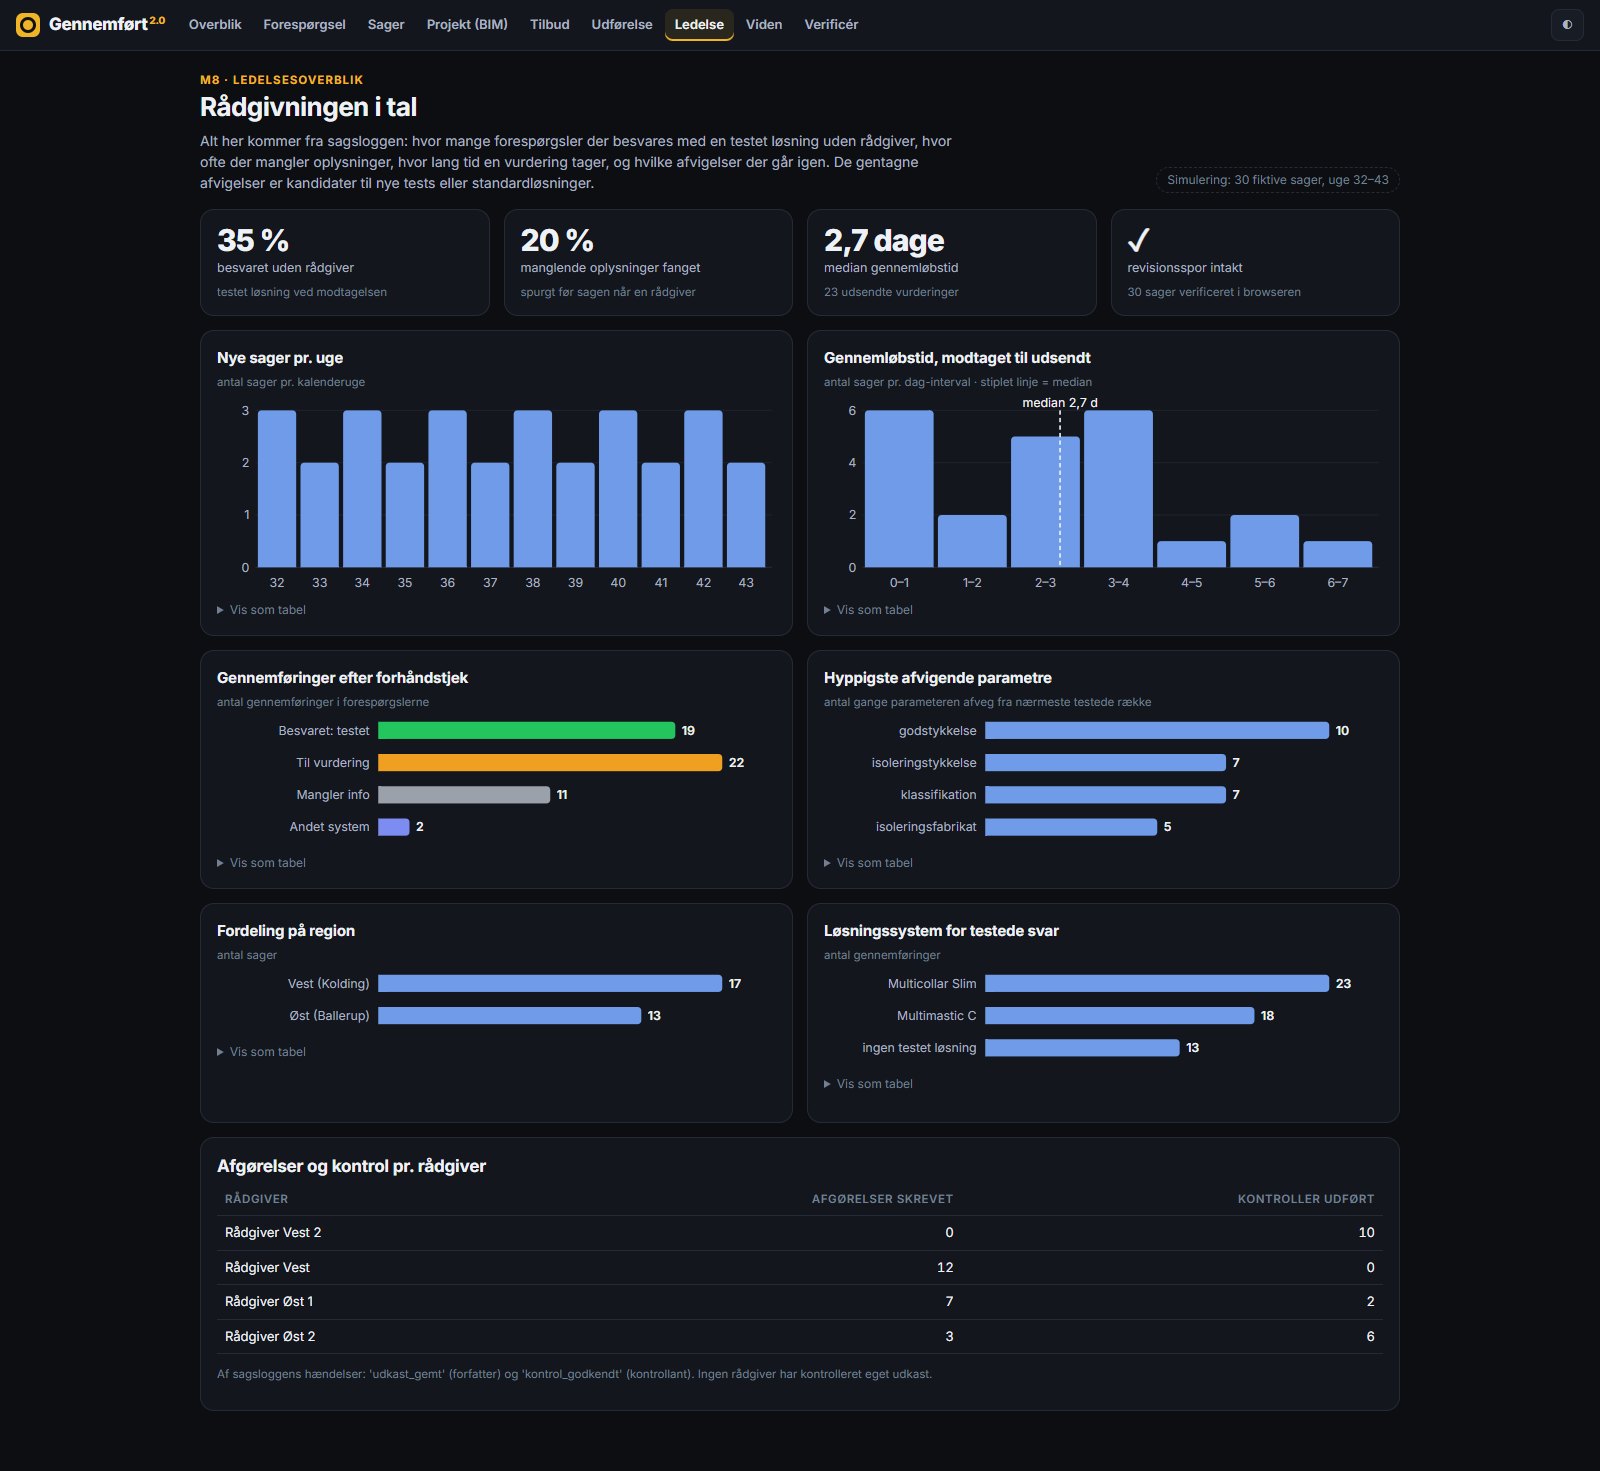
0answered at intake, no adviser needed*
0incl. an end-to-end browser workflow
0in the SHA-256 manifest, re-hashed on every run

* simulation of 30 fictitious cases over 12 weeks.

Tour

Sixty seconds, end to end

Rendered frame by frame from the running app: no screen recording, no cuts in the 3D.

Workflow

Before and after

Same six-point deliverable as today: description, deviation, professional assessment, solution, assumptions, documentation. But each step is data that can be checked and reused.

Today

  1. Free-text formCustomer describes the task, attaches drawings.
  2. Follow-upAdviser calls for missing sizes and brands.
  3. PDF lookupTested set-ups found by hand, system by system.
  4. WordArgument written from scratch; precedents from memory.
  5. PDF sentNo link to the project, revisions or execution.

With Gennemført 2.0

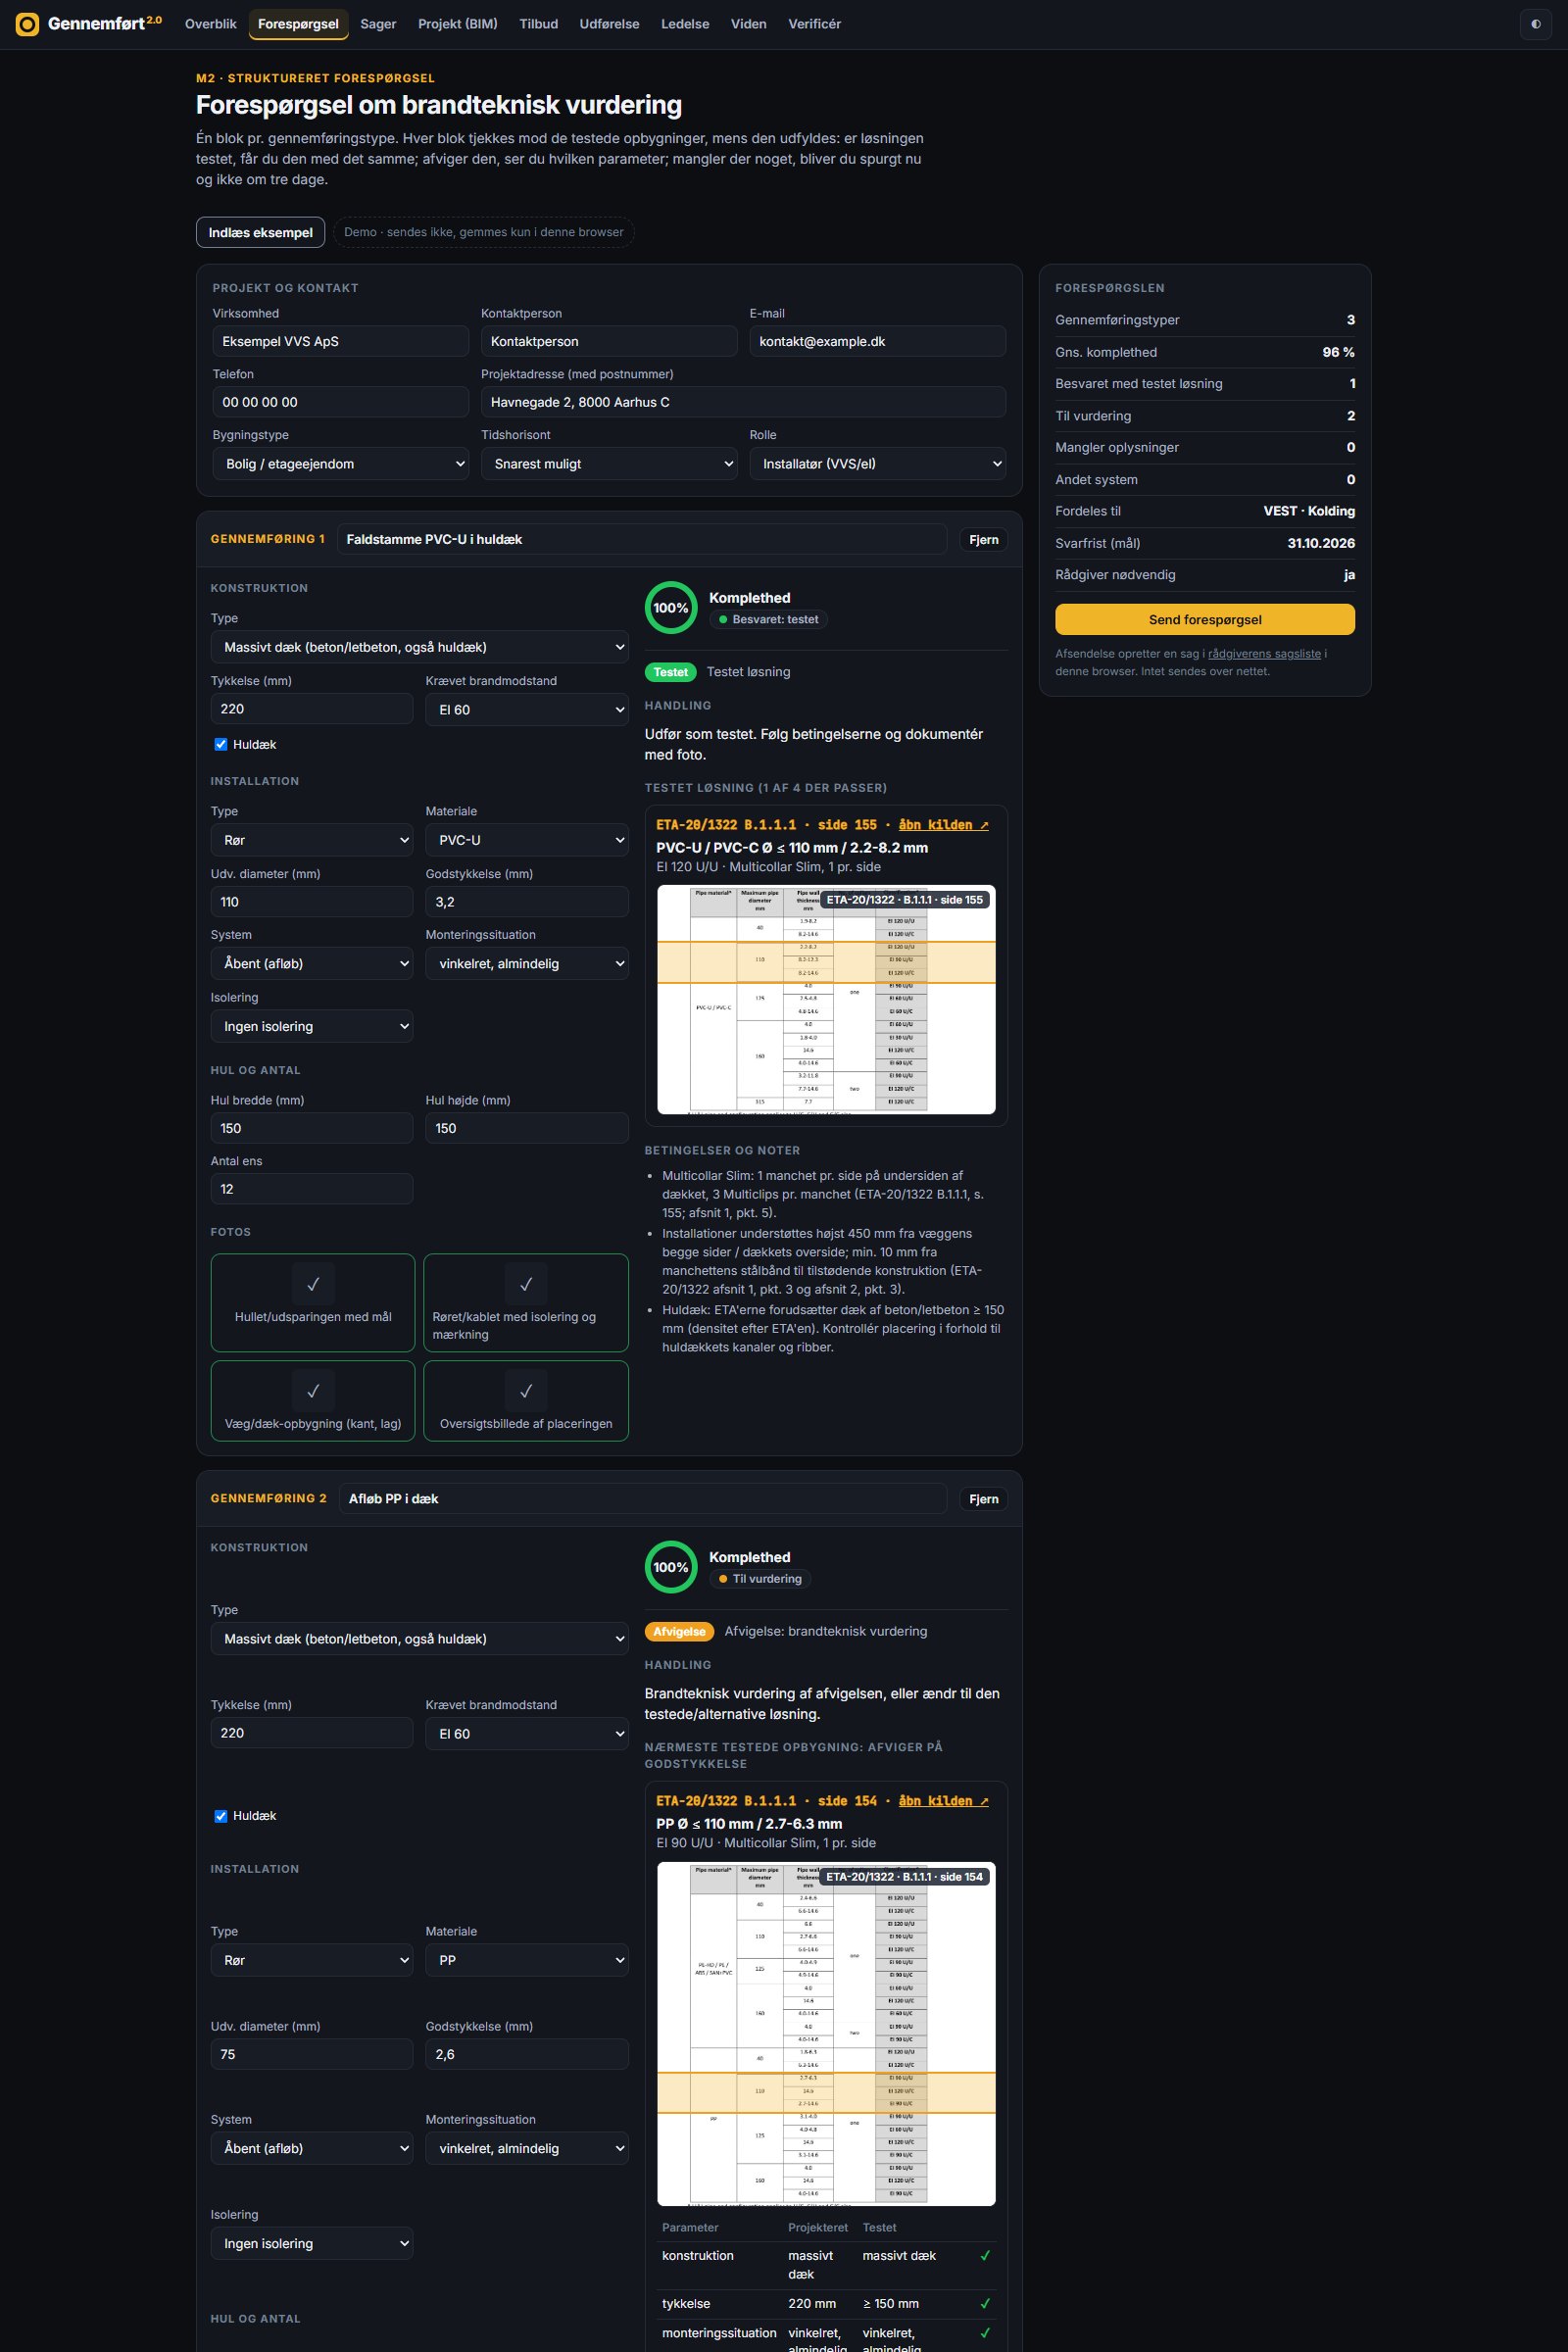
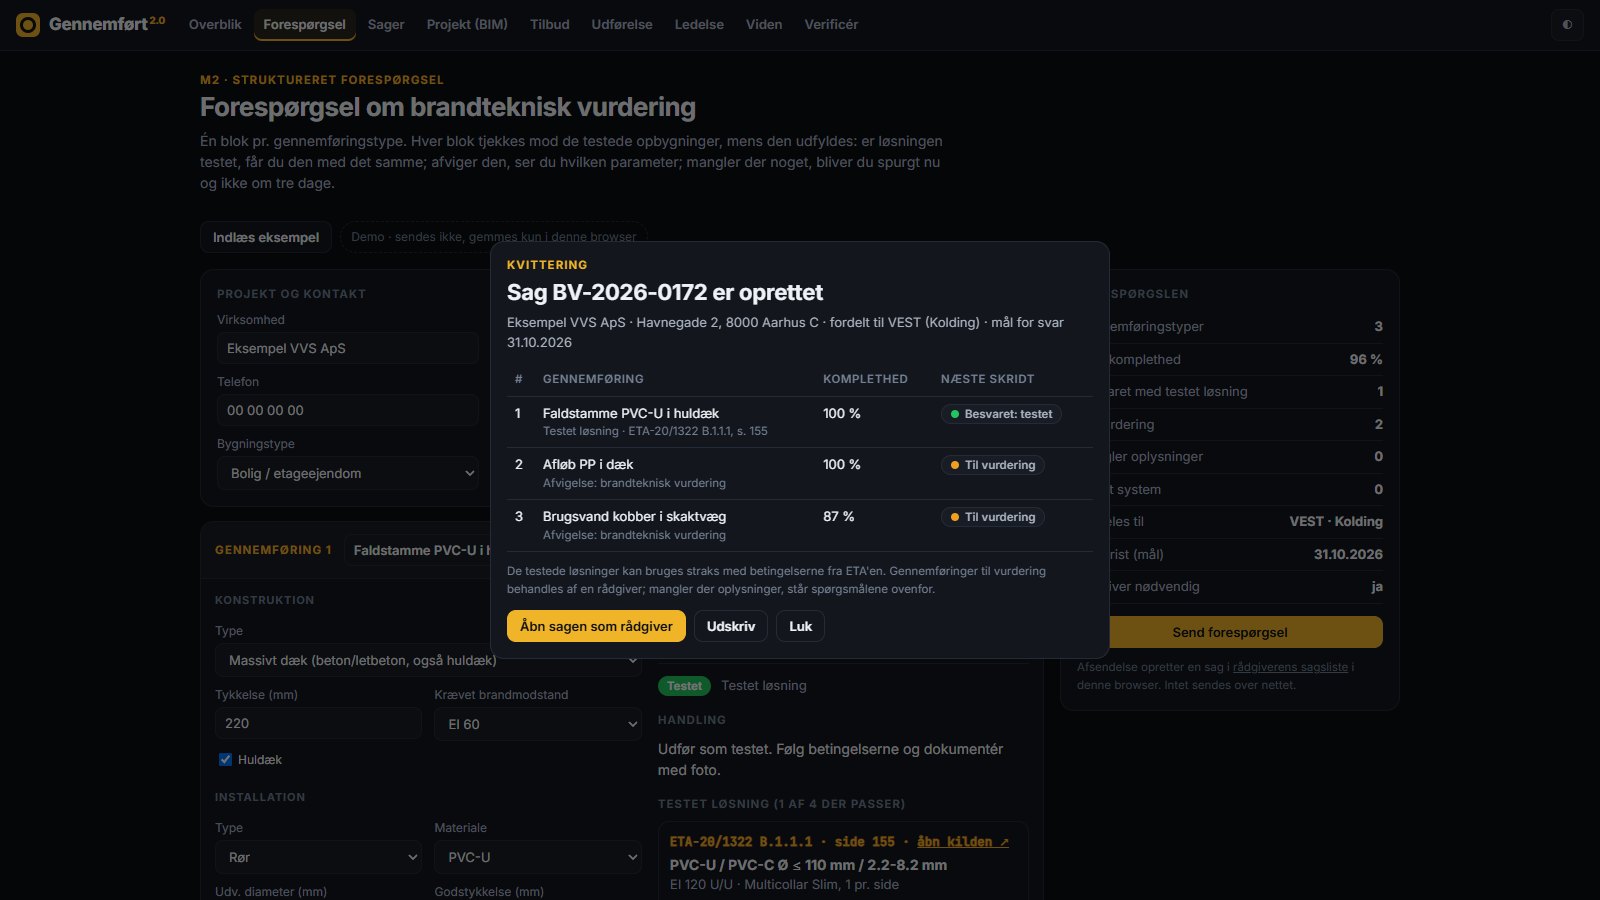
  1. Structured enquiryFields per penetration, photo checklist, live pre-check.
  2. TriageTested set-ups answered at once; the rest routed east/west.
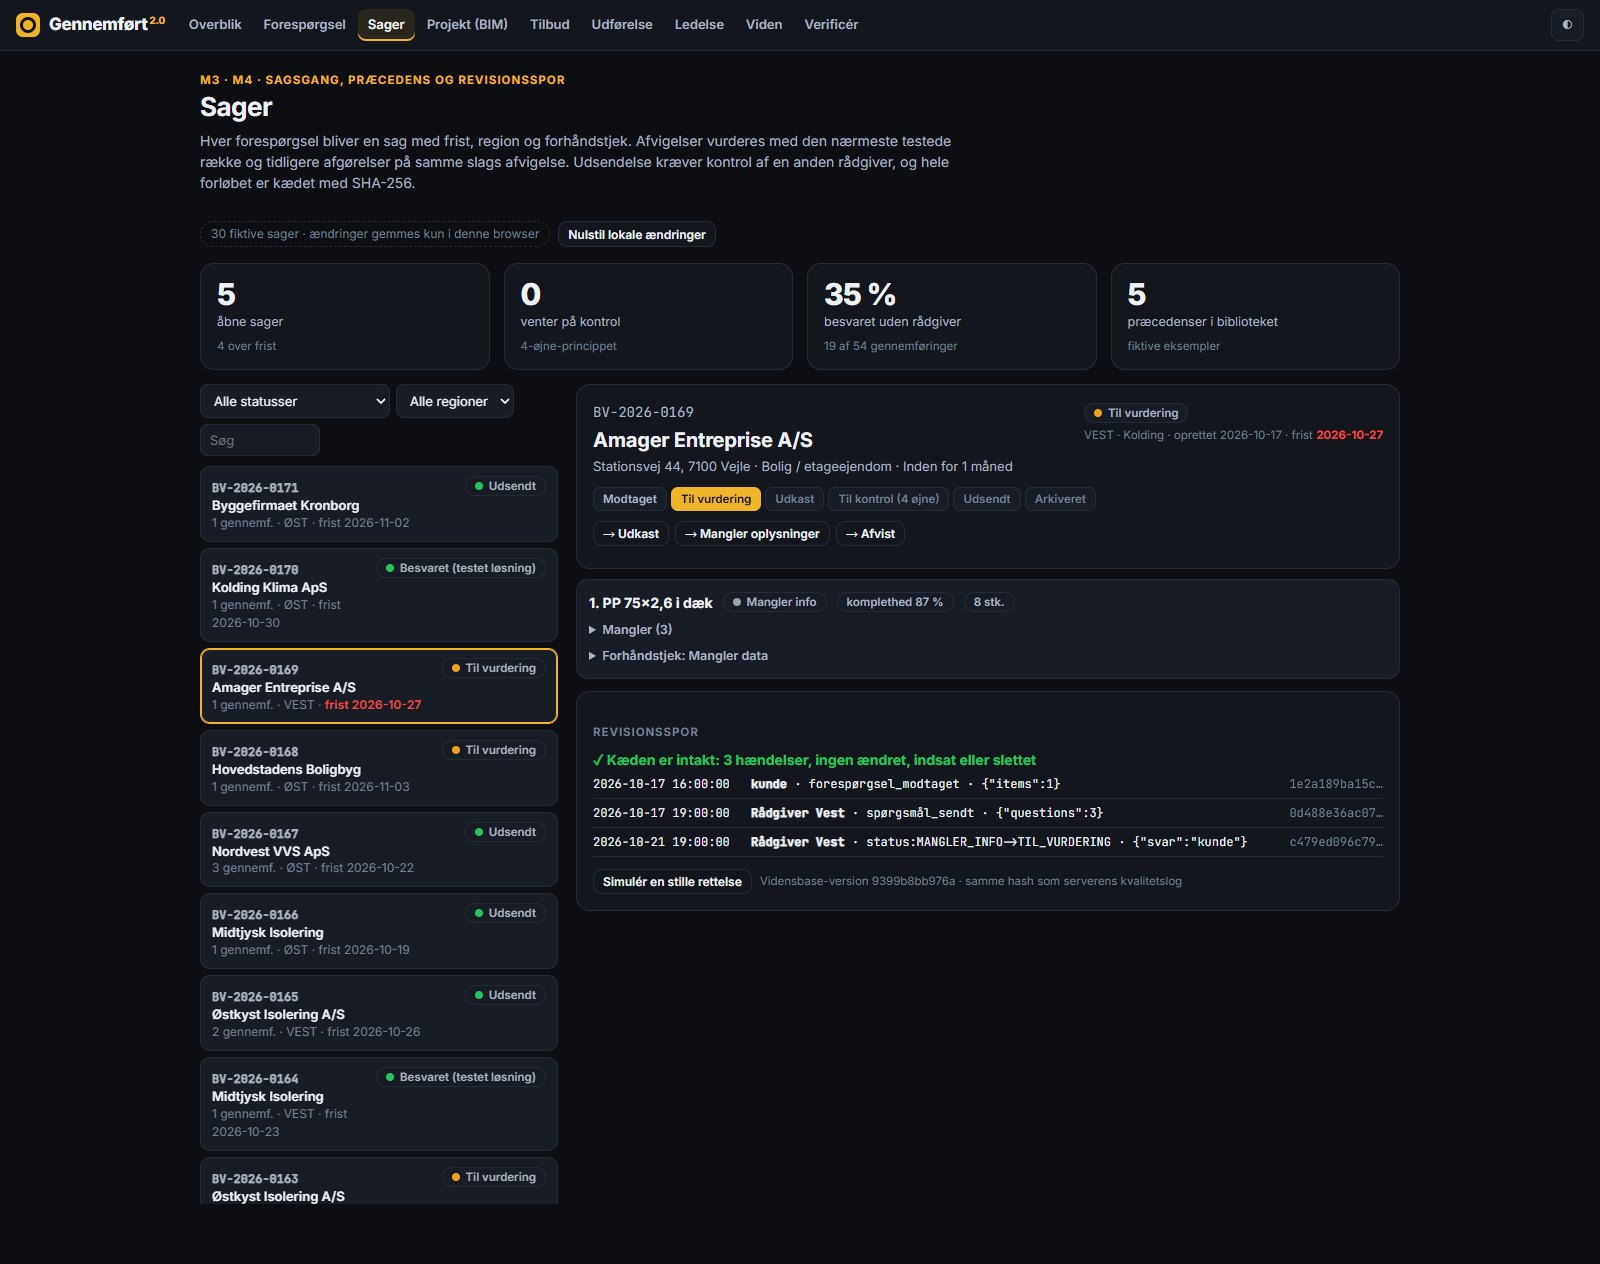
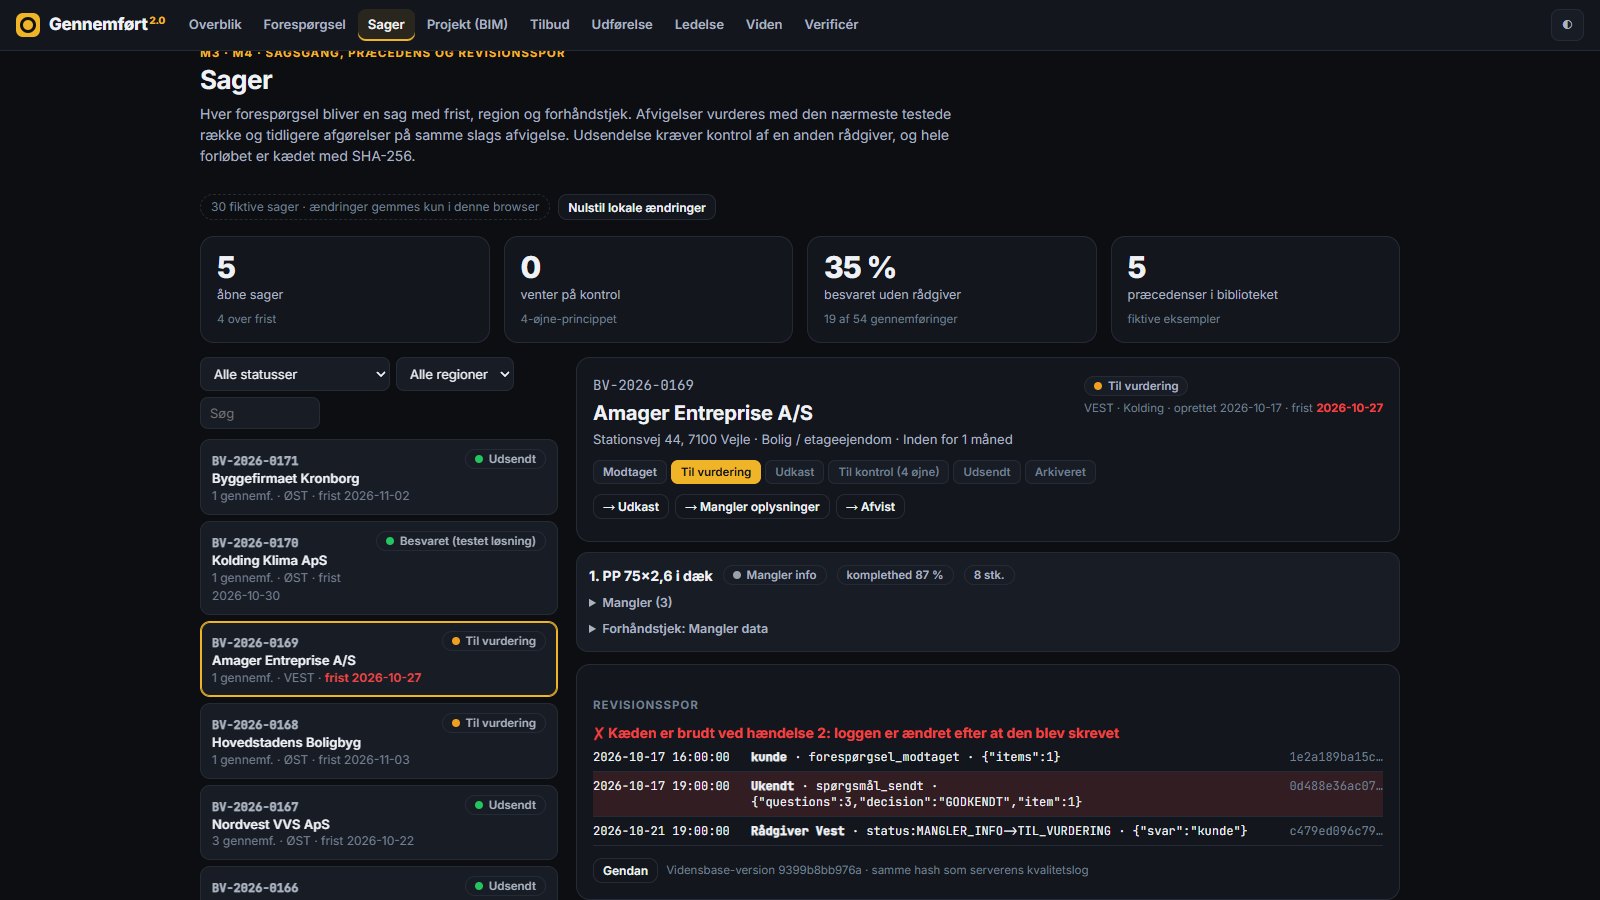
  3. Case + precedentNearest ETA row, deviation signature, earlier decisions.
  4. Decision + four eyesAdviser's own argument; reviewed by a colleague; hash-chained.
  5. Verifiable issuePDF with ETA excerpt, QR code, site checklist, owner package.
Modules

Nine modules, one knowledge base

Verification

Nothing has to be taken on trust

Every output has a check a person can do in minutes, and an automated one that runs on every change.

1The file

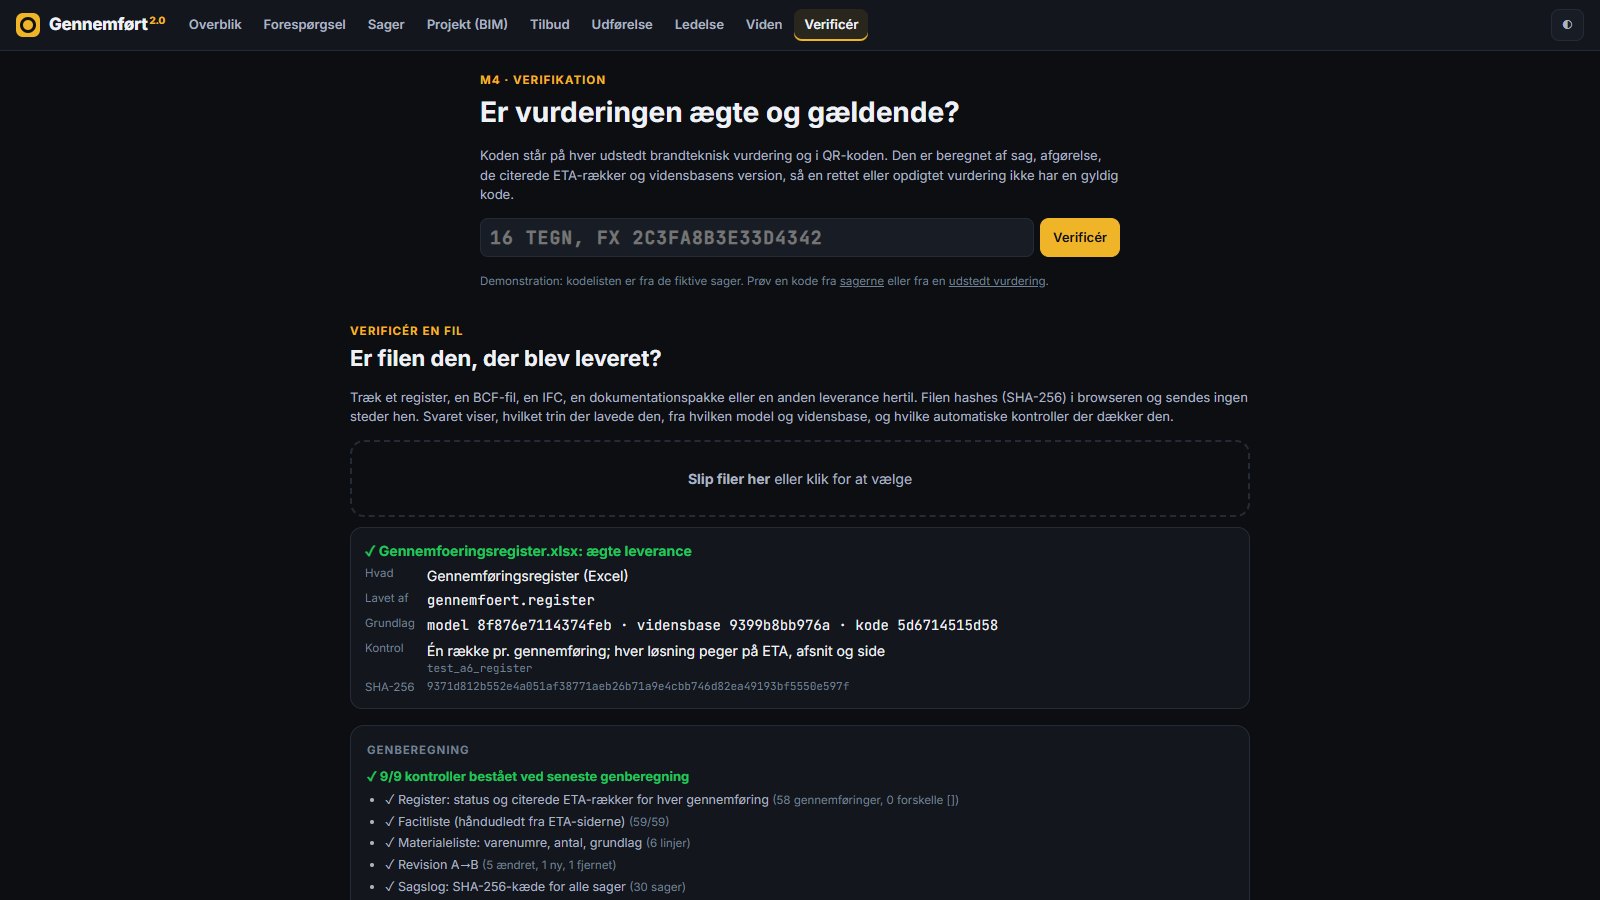
Every deliverable is in a SHA-256 manifest with the step, model, knowledge base and code that produced it. Drag a file onto Verificér; it is hashed in your browser, never uploaded.

2The answer

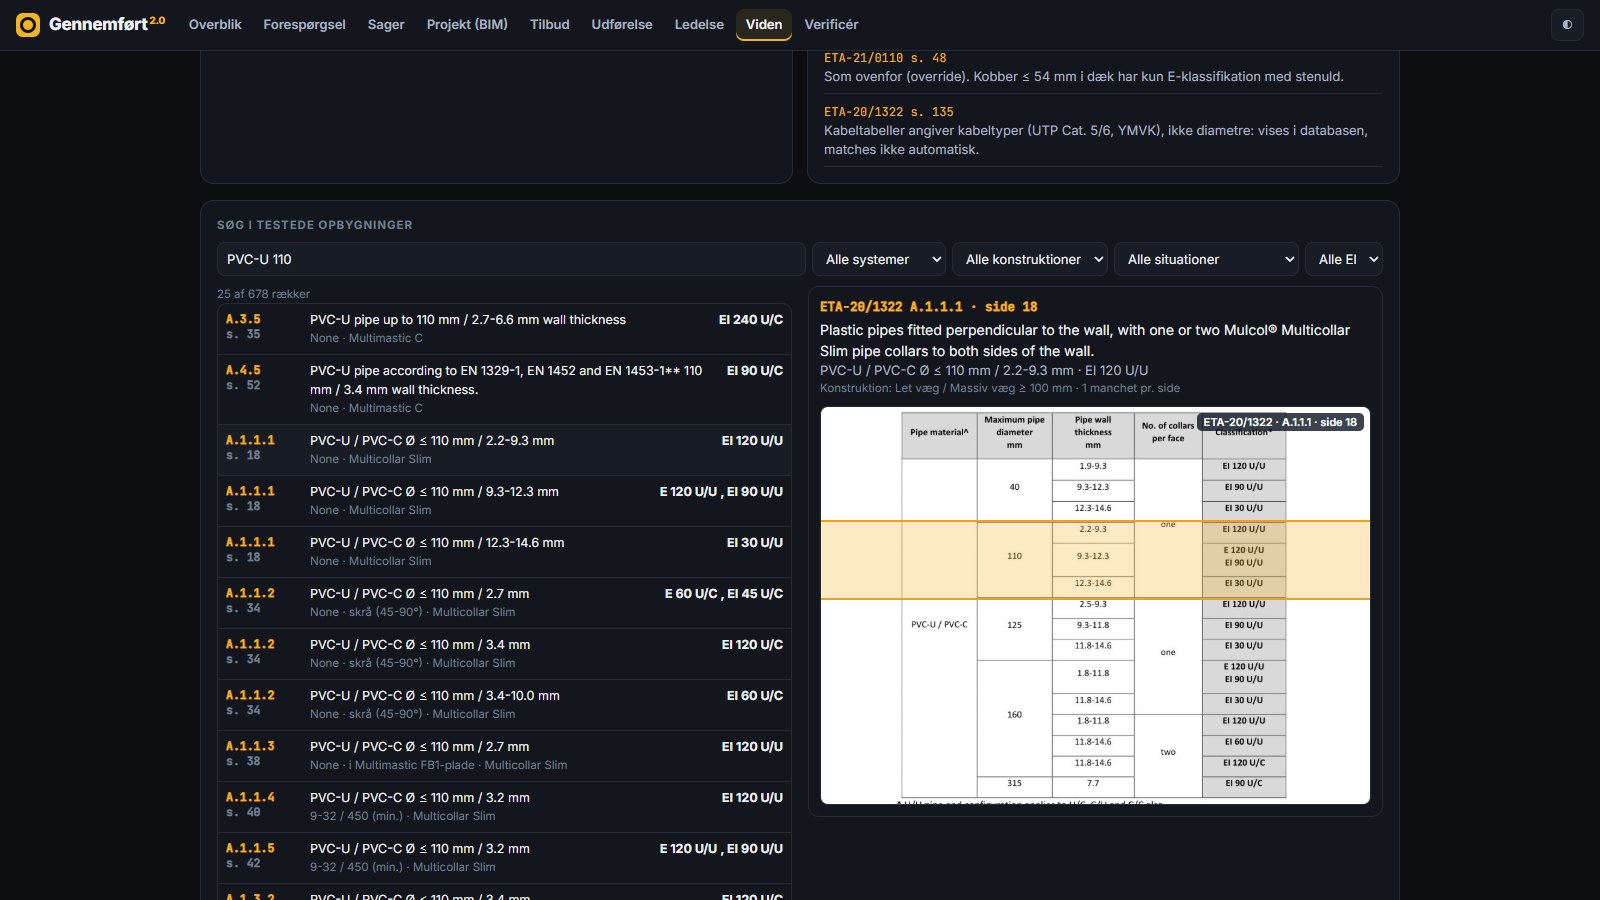
Every verdict shows the ETA page with the tested row highlighted, a link to the official PDF at that page, and each parameter as designed vs tested.

3The method

python -m gennemfoert.reproduce rebuilds everything from the source model and compares it with what is published: 9/9 checks.

File verification in the browser

Output-by-output verification table →

Gallery

Screens

MCP

Ask it from Claude, Copilot or an IDE agent

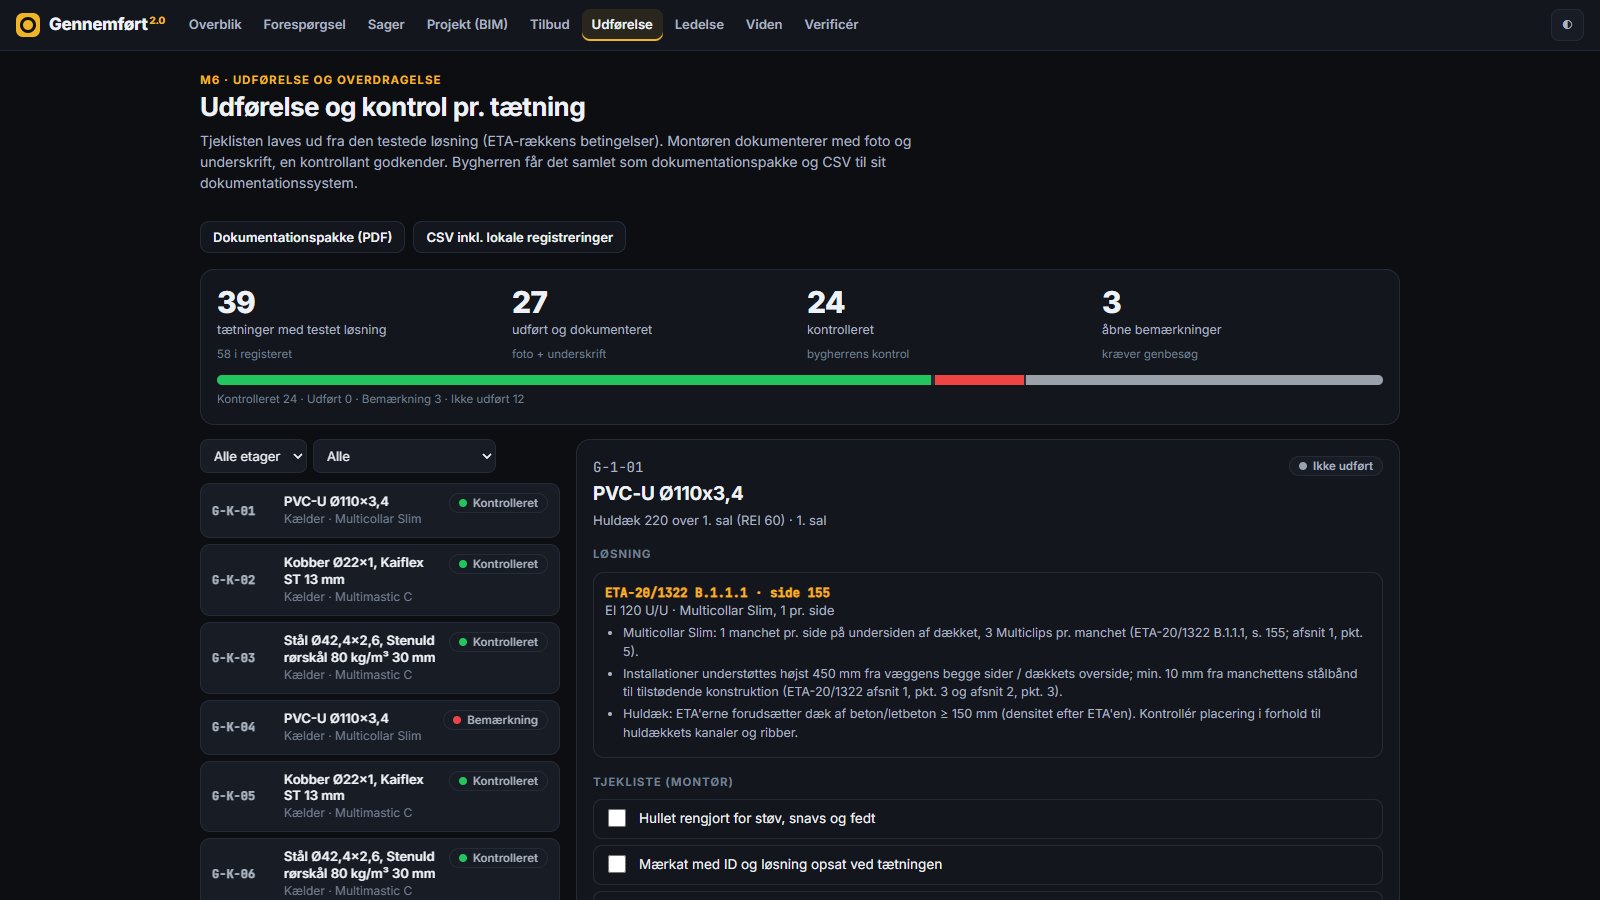
Fourteen tools on the same engine: check a penetration, pre-check an enquiry, find precedents, read a case with its chain status, verify an assessment code, quote, revision impact.

{"mcpServers": {"gennemfoert": {
  "command": "python",
  "args": ["<repo>/src/mcp_server.py"]}}}